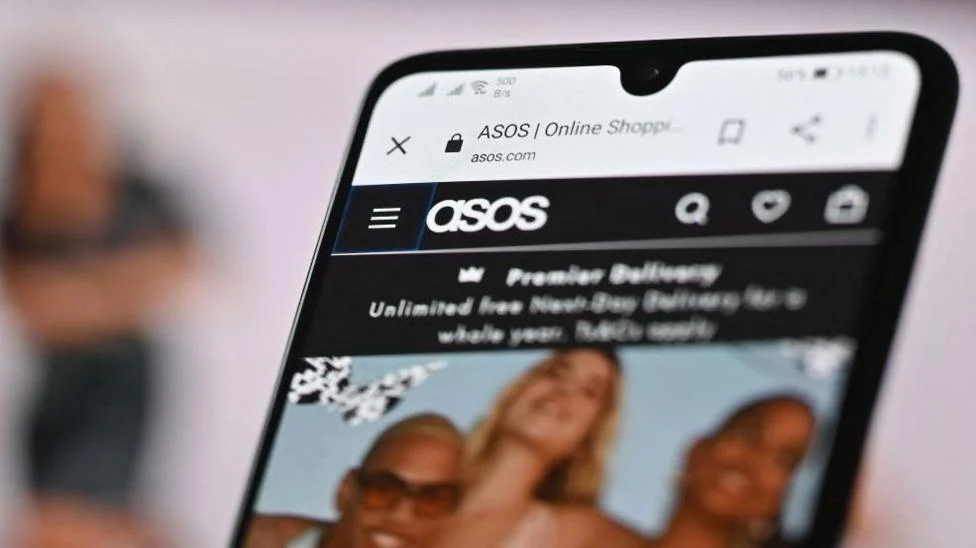
ASOS customers throughout the UK are reporting suspicious pop-up messages sent directly via the company’s mobile application. These notifications, which have appeared on the phone screens of dozens of users, seem to be part of an extortion attempt targeting the retailer. According to dozens of people have, About receiving a strange message from the clothing and beauty store’s app, appearing on their phone screens. Dozens of people have posted about receiving the message – confused as to what it means, on social media.
The message is explicitly addressed to the ASOS data protection officer and IT department. It states: “Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it.” The notice also includes a link to a Telegram channel created by a group calling itself Xuanye Group.
Charlotte Wilson, head of enterprise at the cyber-security firm Check Point, described the incident as a “deeply serious attack.” She noted that it is particularly alarming because the hackers have utilized the company’s own communication channel to deliver a ransom note to users, exploiting the inherent trust customers place in official app notifications.
The mention of a “Snowflake instance” refers to the data storage provider Snowflake, which has been associated with various high-profile security breaches involving organizations like Ticketmaster and Santander. It remains unclear whether ASOS uses Snowflake services or if any sensitive data has been accessed. Whose tools are used by dozens of firms for collecting, analysing and storing data, this refers to the data storage company Snowflake.
Dan Bird of the cyber security firm Horizon3 highlighted the technical implications of the message. He pointed out that broadcasting a push notification to users requires access to the company’s internal notification infrastructure, which is distinct from the Snowflake data platform mentioned in the ransom note. According to Bird, if both assertions made by the attackers are accurate, it would indicate that the intruders successfully obtained credentials providing access to multiple secure systems.
The Xuanye Group appears to be a newly formed entity, with their Telegram channel created on the same day as the incident. The group has maintained minimal activity, with only three posts currently visible, the latest being the claim regarding the ASOS system intrusion.
ASOS did not provide an immediate response to requests for comment regarding the breach. While most cyber extortion cases are handled through private negotiations to ensure discretion, this incident is notable for the public manner in which the hackers have chosen to broadcast their demands to the retailer’s customer base. It is, however, very unusual for a data breach to be revealed quite so publicly – and for customers to be informed in this manner.